Published: October 16, 2026 · Last updated: October 16, 2026
TL;DR: TFG London, the company behind British fashion brands Hobbs, Whistles and Phase Eight, was hit by a cyberattack that knocked out IT systems and online ordering starting October 13. It’s the latest in a growing list of UK and international fashion retailers hit by hackers this year.
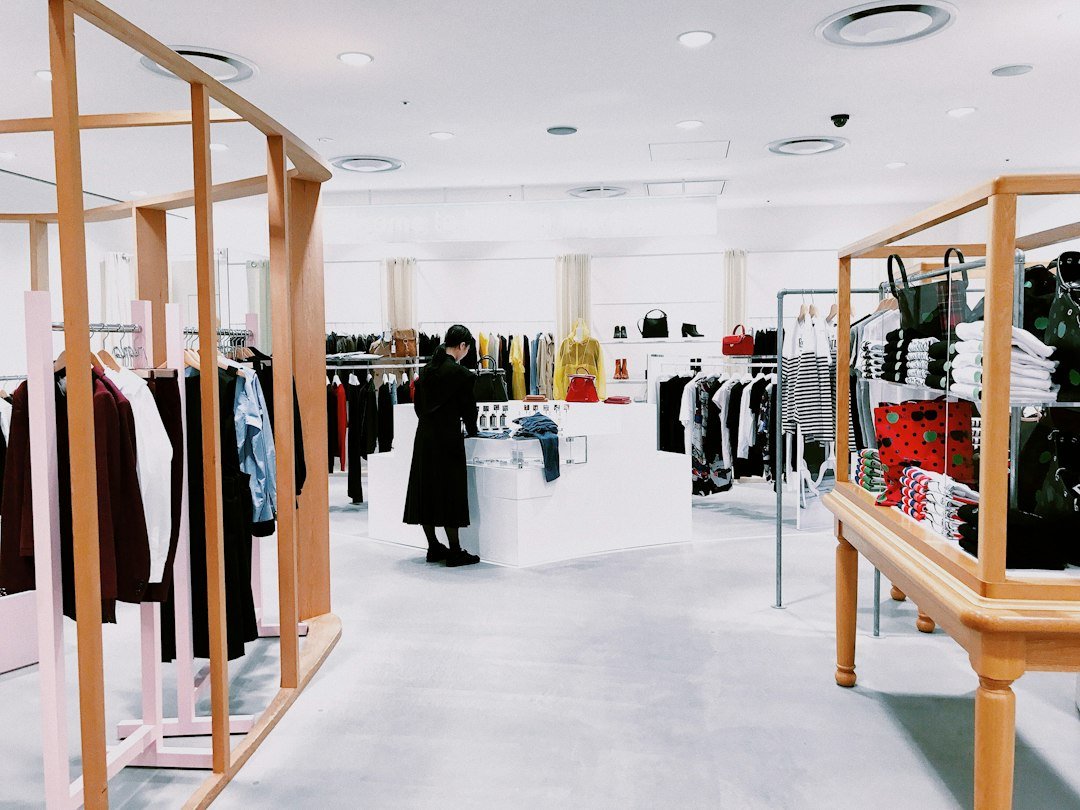
Three well-known names on the UK high street went dark online within the same window this week. Hobbs, Whistles and Phase Eight, all owned by TFG London, confirmed that a cyberattack had disrupted their IT systems starting around October 13, forcing all three brands to apologize to customers over delayed orders, payment issues and intermittent site outages.
TFG London is the UK retail arm of South Africa’s The Foschini Group, one of the larger apparel conglomerates operating across both markets. The company hasn’t published a detailed technical breakdown of the incident, which is typical in the first days after a breach, but confirmed the disruption publicly through statements to ITV News and other UK outlets, and the pattern matches what cybersecurity trade press has been tracking as a wider wave of attacks against fashion retailers.
That wider pattern is the part worth paying attention to. TFG London is not an isolated incident. It’s the latest entry on a list that’s grown uncomfortably long over the past year, UK and international retailers across fashion, apparel, and department stores have been hit by ransomware crews and data-extortion groups at a pace that’s outstripped almost every other retail category. Attackers have figured out something fairly obvious: fashion retailers run on tight seasonal margins, hold huge customer payment databases, and often run older point-of-sale and inventory systems that were never built with modern threat models in mind.
For Hobbs, Whistles and Phase Eight specifically, the practical fallout has been what you’d expect. Customers reported being unable to complete online checkouts, track existing orders, or reach customer service through normal channels for several days. None of the three brands has confirmed, as of publication, whether customer payment data or personal information was accessed, which is the question that actually matters for the roughly unknown number of shoppers who used these sites in the days before the disruption became public.
There’s a quieter lesson in here for smaller retailers too. TFG London isn’t a scrappy startup running on a shoestring IT budget, it’s part of a multinational group with real security resources. If an operation at that scale can still get knocked offline hard enough to apologize publicly across three separate storefronts, the message to every mid-sized e-commerce operator running on a fraction of that budget isn’t subtle: this isn’t a problem that money alone solves, and it isn’t a problem that’s going away.
The honest answer right now is that nobody outside the investigation knows exactly what happened, how the attackers got in, or what data left the building. What’s confirmed is the outage, the apology, and the pattern. The rest will come out in the standard slow drip that follows these incidents, usually starting with a regulatory filing and ending, if history is any guide, with a breach notification letter that undersells the scope for as long as legally possible.
Related: One startup is sending AI agents undercover specifically to catch the scammers behind attacks like this, and Ramp’s record valuation shows how much money is riding on companies getting their back-office systems right.
Bottom Line: Fashion retail has quietly become one of the most targeted categories in cybercrime, and TFG London just became the newest proof point. Until retailers treat security spending with the same seriousness as seasonal inventory planning, this list is only going to get longer.
Follow Teck Hustlers: Facebook · X · Instagram · LinkedIn · TikTok · Pinterest
The Teck Hustlers Editorial Team covers technology, business, finance and gaming news for readers who want the story behind the headline. Every article is researched, written and edited by our in-house team, checked against company announcements, filings and reputable reporting, and updated when new facts emerge. We focus on what each development means for founders, professionals, investors and everyday users. Have a tip or a correction? Reach us through our contact page.